· Cyber Security · 4 min read
Both computers work, but are they both secure?
2 computers can look identical and work perfectly while presenting very different cyber risks. Working IT does not necessarily mean secure IT.
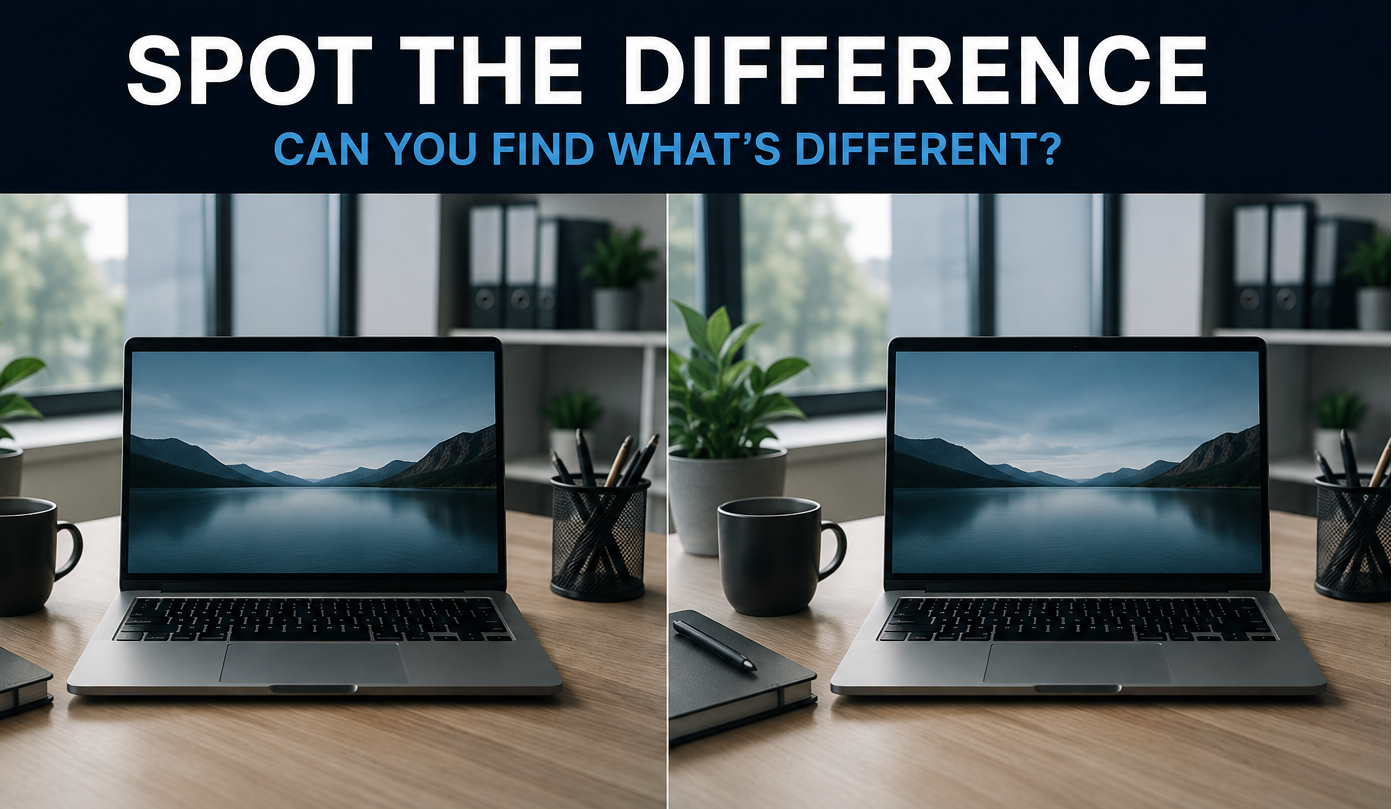
At first glance, the 2 computers above look identical.
Both power on, both connect to the internet, both send and receive emails, both run the software their users need. Neither appears to have anything wrong with it. So which computer represents the greater cyber risk?
From looking at them, you probably cannot tell and that is exactly the point.
Cyber risk is often invisible
When something is physically broken, we normally know about it.
- A broken bone, gets a medical help.
- A car with a warning light gets serviced.
- A leaking pipe gets fixed.
- An alarm gets a response.
- A laptop that refuses to start gets reported.
- A server that goes offline quickly becomes somebody’s problem.
Cyber security is different.
A computer can appear to be working perfectly while still having significant security weaknesses. One of those computers could have:
- Missing security updates
- Weak or reused passwords
- No Multi-Factor Authentication
- Unsupported software
- Poorly configured email security
- Excessive user permissions
- Backups that have never been tested
- Security software that is disabled or out of date
The other computer could be fully patched, properly configured and protected with strong security controls. Yet to the person using them, both machines may appear exactly the same.
Working IT does not necessarily mean secure IT
This is an important distinction for business owners, trustees and senior leaders. It is very easy to judge technology by whether it works.
- Can staff log in?
- Can they access their files?
- Is email working?
- Can customers use the website?
- Can invoices be sent?
If the answer to those questions is yes, everything can appear fine. But operational availability and cyber security are not the same thing.
A device does not need to display a warning saying: “This computer is vulnerable.”
Some of the weaknesses that matter most can sit unnoticed for months or even years while the system continues operating normally.
That creates a dangerous assumption: “Everything is working, so everything must be OK.”
It may not be.
The questions organisations should be asking
Instead of asking only: “Is our IT working?”
Organisations should also ask: What technology do we actually have?
You cannot effectively protect systems, software and devices that nobody knows exist. Maintaining an accurate understanding of your technology estate is one of the foundations of good cyber security.
Is it supported and up to date?
Security updates matter. So does identifying operating systems, applications and devices that have reached end of support. Unsupported technology may continue working perfectly well while no longer receiving important security fixes.
Who has access?
Users should have the access they need to do their jobs. They should not automatically have administrator privileges or access to systems they no longer need. Old user accounts, unnecessary permissions and excessive privileges can all increase risk.
How are accounts protected?
Strong, unique passwords or passkeys are important.
Multi-Factor Authentication adds another important layer of protection if a password is stolen or compromised.
For many organisations, enabling MFA is one of the most valuable security improvements they can make.
How is email protected?
Email remains one of the most common routes into an organisation.
Phishing, impersonation, credential theft and business email compromise all rely heavily on email.
Controls such as SPF, DKIM and DMARC can help protect your organisation’s domain and reduce opportunities for impersonation.
Could we recover?
Having a backup is not the same as being able to recover from one. Backups need to be protected, monitored and tested.
The important question is not: “Do we have backups?”
It is: “Could we successfully restore our systems and data if we needed to?”
Cyber Essentials provides a practical starting point
For many UK organisations, Cyber Essentials provides a useful framework for addressing common technical risks.
Rather than trying to protect against every possible cyber threat, Cyber Essentials focuses on fundamental controls that can reduce exposure to common attacks. These include:
- Firewalls
- Secure configuration
- Security update management
- User access control
- Malware protection
The value is not simply obtaining a certificate. The real value comes from understanding your environment, identifying weaknesses and improving the way your systems are protected.
Security should be measured, not assumed
The 2 computers in the image could sit next to each other every day. They could perform exactly the same job. To the people using them, they could appear identical. But underneath the surface, their security posture could be completely different. That is why cyber security cannot be judged by appearances.
Both computers work.
The more important question is: How do you know they are both secure?
Cyber risk is often invisible. You discover it by asking the right questions, understanding what technology you have and checking whether the right controls are actually in place. Do not wait for something to break before you start looking.
Need help understanding your cyber risk?
White Rock Advisory helps organisations understand their cyber risk, strengthen practical security controls and improve cyber resilience without unnecessarily complicating their technology.
If you are unsure what risks may be sitting unseen within your organisation, start by understanding what you have, how it is protected and where the gaps are.
Talk to White Rock Advisory today.
Know your risk. Reduce your risk. Build resilience.